This summer, the people who disrupted American water did not need a clever new exploit. They needed controllers that anyone could reach from the open internet, and they found plenty of them. The good news is that most of the fix is plain work. You learn what you own, you take it off the internet, and you decide who gets to touch it. This piece explains what happened, why small and mid-size utilities make the softest targets, and what a CEO should be ready to sign before the next round.
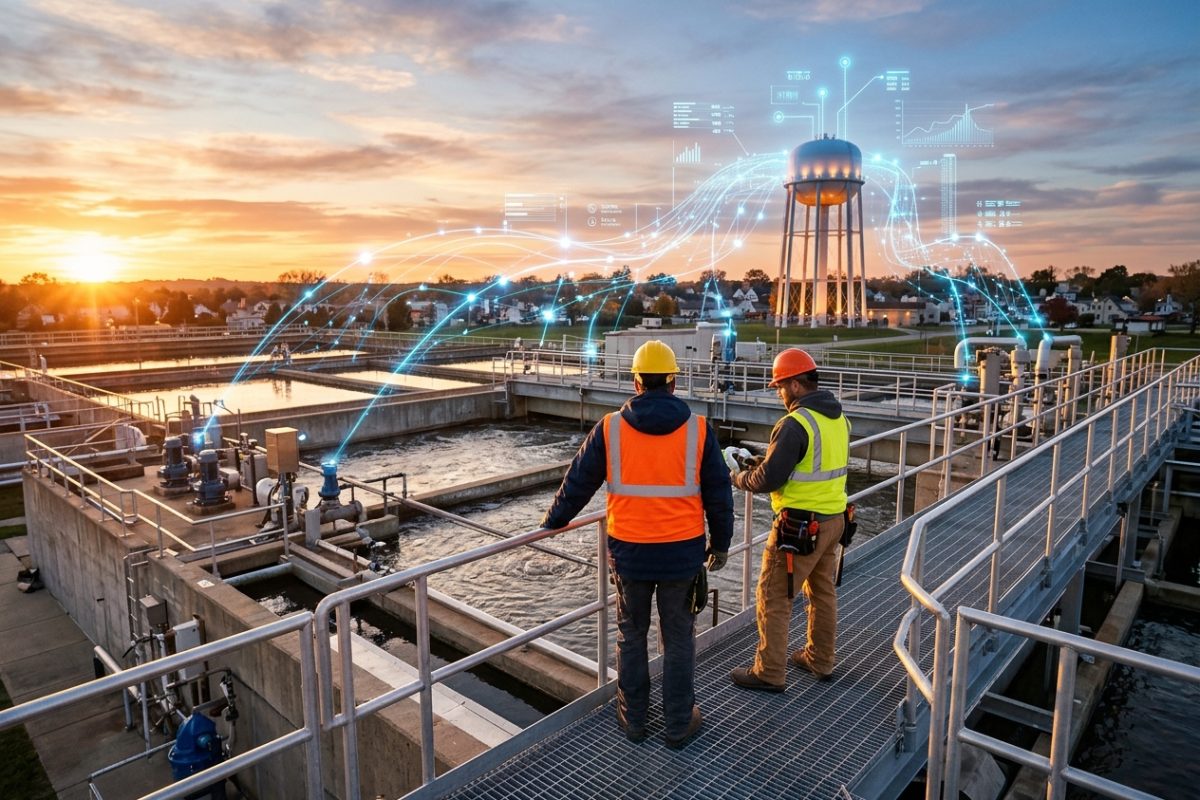
Picture a Sunday night in late July. The operator on duty at a small treatment plant hears an alarm, looks up, and watches the screen stop making sense. By morning the plant is offline and the city is asking residents to go easy on water. Nobody stole a database. Nobody left a ransom note. Someone reached a small box on the internet and changed its settings.
What Happened in Minnesota
On July 26 and 27, 2026, a coordinated attack hit the control systems of community water systems across Minnesota. The state’s IT agency, MNIT, said “more than 30 water systems throughout the state were impacted,” as The Hacker News reported, and the effects varied from town to town.
The details read like a set of small-town bad days. According to The Hacker News, Braham’s water plant went offline, and the city asked residents to limit use until treatment resumed. In Plymouth, two water towers and several wastewater lift stations lost their cellular links, and staff kept things running by hand. Maple Plain’s automated controls were hit, and the city declared a local state of emergency. South St. Paul’s controls were affected, but service continued.
Notice what those four towns have in common. None of them lost data in the way a bank or a hospital would. They lost sight and control of physical equipment, which is a different kind of loss. You can restore a file server from last night’s backup. You cannot restore last night’s water pressure.
No official body has named the attacker. The security firm Tenable told The Hacker News that the timing and pattern fit the methods tied to CyberAv3ngers and other Iran-linked groups. A later summary from the law firm Foley Hoag notes that news outlets reported claims of responsibility from groups calling themselves APT IRAN and CyberAv3ngers. Those are claims, not findings, and you should treat them that way. For the purpose of protecting your plant, the name matters less than the method, and the method was not subtle.
Seven States and One Controller Family
Minnesota was not alone. On July 30, the FBI and EPA warned that utilities in at least seven states had reported incidents since July 27 involving internet-facing Rockwell Automation (Allen-Bradley) MicroLogix 1100 and 1400 controllers, according to summaries by The Hacker News and Foley Hoag. These are programmable logic controllers, or PLCs. They are the small industrial computers that open valves, start pumps, and keep a tank from running dry. Most of them were designed for a closed room, not for the open internet.
As those summaries describe the warning, attackers reached the exposed PLCs remotely and changed their network addresses and passwords. Operators lost the ability to see and steer their own equipment. Some sites saw pressure loss and flooding, and the FBI cautioned that low pressure can let untreated groundwater into pipes. At least one utility found altered project files after noticing that its control logic did not match from site to site. The agencies did not name the states, and they did not tie this activity to Minnesota. You should not assume a link either, though the timing invites one.
Around the same time, CISA expanded an advisory, AA26-097A, on Iran-affiliated actors targeting internet-facing PLCs from several makers, including Rockwell, Schneider Electric, and Siemens. As The Hacker News and Foley Hoag summarize it, the behavior described is worse than a lockout. It includes changing control logic, faking what operators see on their screens, and switching off the shutdown and alarm logic that exists to catch exactly this kind of trouble. Foley Hoag adds that affected devices often still had default credentials or weak separation from other networks.
The attackers did not need to break in. In many cases, the door was already open.
The attackers did not need to break in. In many cases, the door was already open.
That sentence is uncomfortable, but it is also hopeful. A door left open can be closed. Unlike a novel exploit that waits on a vendor patch, most of this summer’s exposure sat inside the utility’s own control. The same lesson runs through the broader vulnerability picture: the most damaging weaknesses are often the oldest and plainest ones.
Why the Small Utility Is the Soft Target
Large utilities have security teams, real budgets, and in many cases years of regulator attention. A town of a few thousand people often has a handful of operators, a contractor who set up the controls years ago, and a cellular modem bolted to a tower so someone can check levels from home. That modem is a convenience. It is also a front door, and nobody wrote down that it was there.
The rules leave a gap as well. Under the Safe Drinking Water Act, community water systems serving more than 3,300 people may have to complete risk and resilience assessments that address cyber risk, per Foley Hoag. Many of the towns in the news this summer sit near the size where that pressure is light or absent. The smallest systems face the least outside scrutiny and often carry the least inside capacity, which is the worst combination on both counts.
The pattern is not limited to water. Mid-market utilities in electric, steam, gas, and waste share the same habit wherever field devices were set up for remote access and then forgotten. Our view of where the electricity business is heading points toward more connected equipment, not less, which means the inventory problem grows every year you leave it alone.
Consider an illustrative case, not a real one. A regional utility with a few hundred employees has a capable IT team, a modern firewall, and a clean audit on its office systems. Out in the field, though, a pump station runs on a controller an integrator installed years ago, reachable through a cellular modem on a public address so the integrator could support it remotely. The IT team does not know the modem exists, because it was never part of their network. Operations assumes IT has it covered. Both are acting in good faith, and the gap between them is exactly where this summer’s attackers walked through.
None of this takes a nation-state budget to fix. It takes someone owning the list.
The Rule That Is Coming
The Cyber Incident Reporting for Critical Infrastructure Act, known as CIRCIA, passed in 2022. Federal News Network reported in July that once its final rule takes effect, covered entities will have to report substantial cyber incidents to CISA within 72 hours and ransom payments within 24 hours. The same report said the rule covers sectors including electric utilities and water systems, and that CISA was aiming for September 2026.
That date slipped. Paubox reported in early October that CISA sent the final rule to the White House budget office for review on October 1, that the text is not yet public, and that the effective date will be set by the rule itself. The HIPAA Journal expects publication before year end. As of this writing, then, the rule is not in force, and you do not yet know exactly who it will cover or when it starts.
The uncertainty is not a reason to wait. Ask yourself a simple question. If your controllers were touched tonight, could your team tell you within three days what happened, which devices were affected, and whether anyone changed the logic? A utility that cannot answer that today will struggle when the clock becomes a legal one. The reporting window is short because the useful window for response is short, and a regulator’s deadline only formalizes a pressure the plant already faces.
The One-Page Check
CISA’s guidance, as summarized by Foley Hoag and The Hacker News, comes down to a short set of commitments. We would put them on a single page and ask the CEO to sign it only once each statement is true. The value is not in the signature. It lies in the work a signature forces into the open.
The page begins with inventory. You keep a current record of every controller, modem, and remote access path in the field, with a named owner beside each one, and anything not on the record is assumed to be exposed. From there the page moves to reach. No control device can be contacted directly from the internet, and remote access runs only through a secure gateway, jump host, or VPN, and only from known engineering laptops.
Next comes identity. Every default password is gone, replaced with strong and unique ones, and any shared login has a person’s name attached to it. The cellular modems get the same care; they require strong sign-in, they are kept up to date, and their connection logs are switched on and actually read by someone.
The last three commitments concern recovery. You hold a clean, tested copy of each PLC’s program, stored off the device, and you compare the running logic against it on a schedule. You have practiced running the plant by hand within the past year, and you know how many hours or days you can sustain it. And you know who calls the FBI, CISA, your regulator, and your counsel, and you could file a report within 72 hours if you had to.
One caution from the guidance deserves its own paragraph. Confirm that the clean backup exists before you pull a PLC off the network. If an attacker has already changed the password, that backup may be your only way back in, and disconnecting first can turn a recoverable problem into a long one.
The signature is not the point. The list behind it is.
The signature is not the point. The list behind it is.
If your office systems already follow a basic information security checklist, this page will feel familiar. The difference is where it applies. Most such lists stop at the edge of the corporate network. This one starts at the pump station.
How to Read the Answers
When the check comes back, the useful question is not how many items are true. It is which ones are false, and why. A missing inventory is the most serious gap, because every other commitment depends on it; you cannot secure a modem you do not know you own. A missing manual-operation drill is close behind, because it measures how long you can absorb a bad night without harm to the public.
Watch for answers that are technically true but practically hollow. A statement that logs are “enabled” means little if nobody has opened them in a year. A backup that has never been restored is a hope, not a backup. A list of owners that names a contractor who left years ago is a list of ghosts. Ask to see the evidence once, calmly, and the quality of every later answer tends to improve.
What This Will Not Do
This check will not stop a determined, well-funded attacker who has been inside your systems for months. It does not replace a real program for securing operational technology, and it does not substitute for the engineering judgment of the people who run your plant. What it does is close the doors this summer’s attackers actually used, and give your board a clear yes or no on each one.
Three Questions for Monday
Ask your operations lead three things. Which of our field devices can be reached from the internet today, and how do we know? When did we last change the passwords on our controllers and modems? If we lost our screens tonight, how long could we run by hand?
If those answers take more than a day to gather, that delay is itself the finding. Innovation Vista is vendor-neutral; we sell advice, not firewalls, modems, or monitoring tools. An independent assessment can map your exposure and help you build the one-page check, drawing on a bench of more than 450 former CIOs, CTOs, and CISOs, including leaders who have run technology in regulated industries. It starts with the same three questions.
The doors this summer were basic. So is closing them.
The doors this summer were basic. So is closing them.